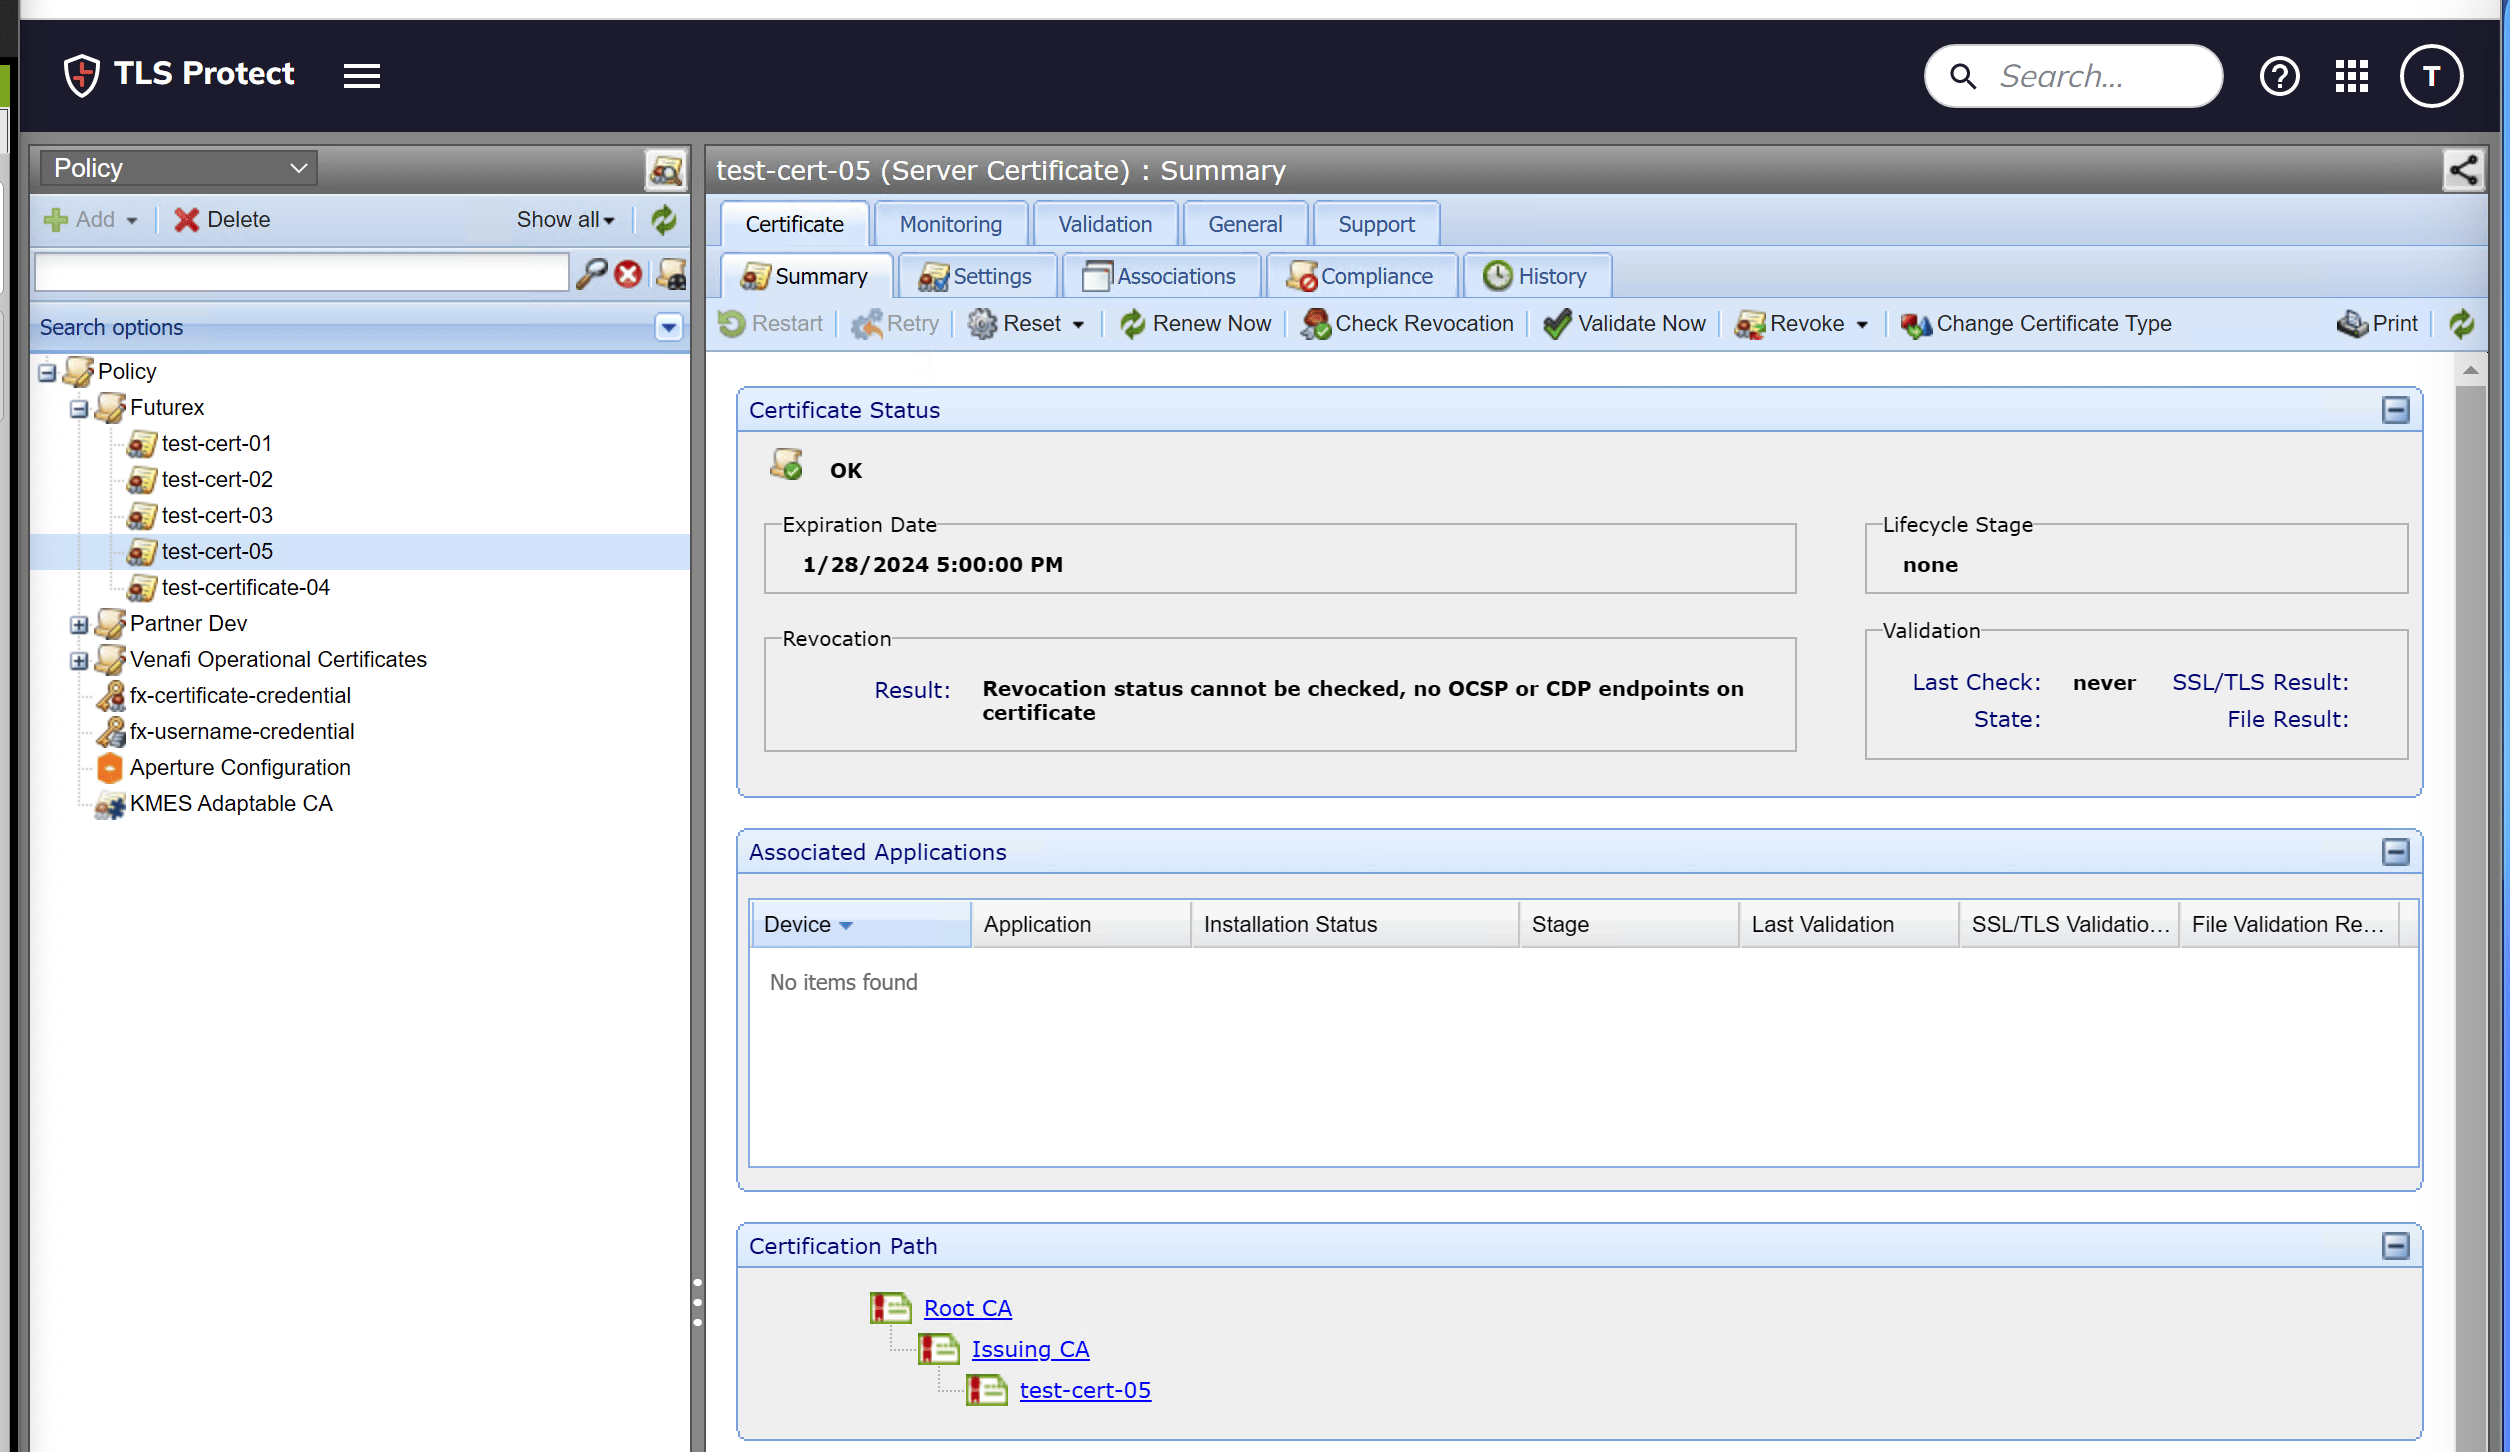
Initiate a certificate request through the Venafi TPP web UI
1
Log in to the Venafi TPP web UI.
2
Select Inventory > Certificates in the main menu.
3
Select [ Create a New Certificate ].
4
In the Certificate Folder drop-down menu, select the certificate policy you created in the previous section, then specify the required values in the fields that populate. When finished, select [ Next ].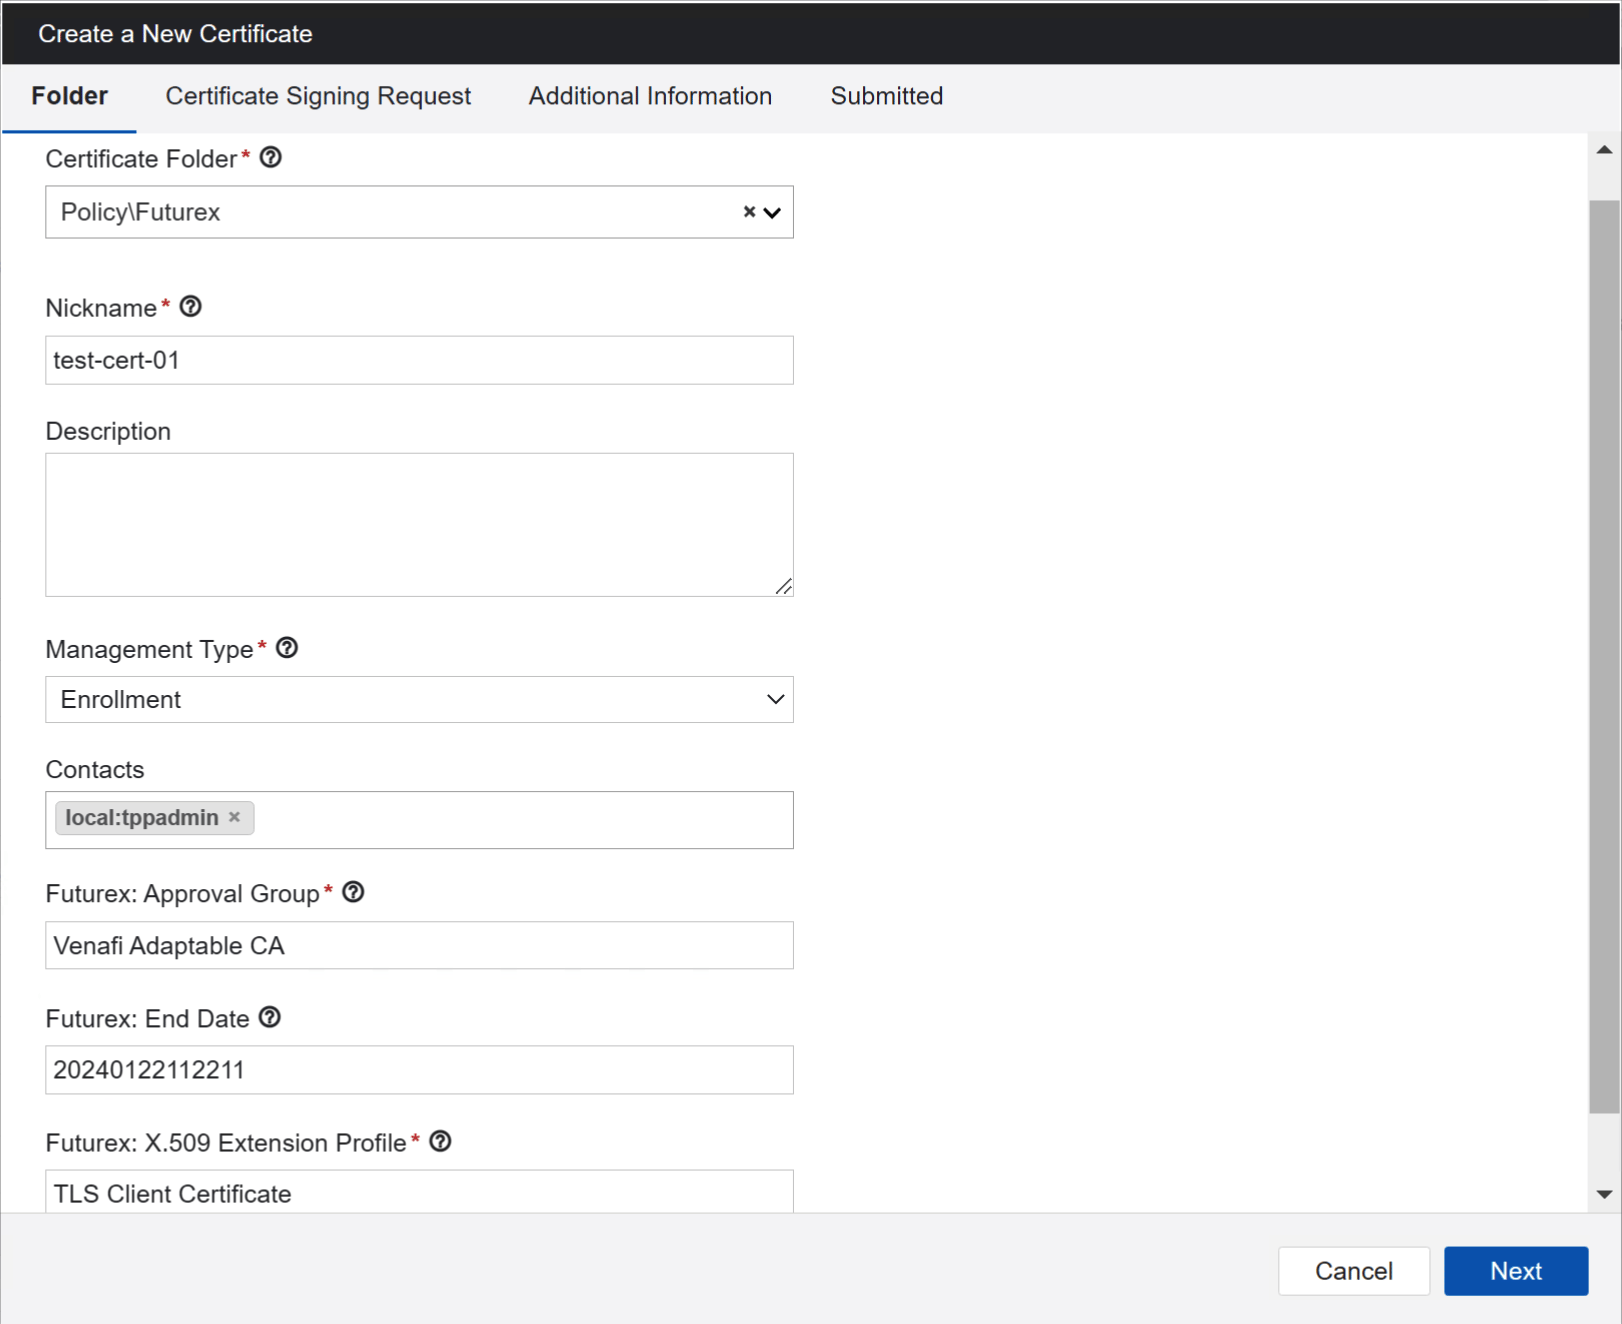
You must select Enrollment as the Management Type.
Multiple formats are valid for specifying the Validity Period (for example, 1 year, 1y, 2 years, 2y, 1month, 1mo, 3 weeks, 3w, 1week, 1 weeks, 10d, 10 days).
5
In the CSR Generation drop-down menu, select Generate a CSR for me, specify all desired values for the Certificate Signing Request, then select [ Next ] when finished.
6
Specify any additional information you wish to include in the request, such as Subject Alternate Names (DNS). Then, select [ Create Certificate ]. You should see a message stating the certificate request has been submitted.
The Subject Alternate Names (SANs) you specify must be in URI format.
Approve the certificate request in CryptoHub
To approve the certificate request on the CryptoHub, perform the following steps:1
Log in to the CryptoHub web UI with the dual-control administrator identities.
2
Go to Administrative Services > PKI Management > PKI Signing Approvals. You should see the certificate signing request inside the approval group created for the Venafi Adaptable CA service.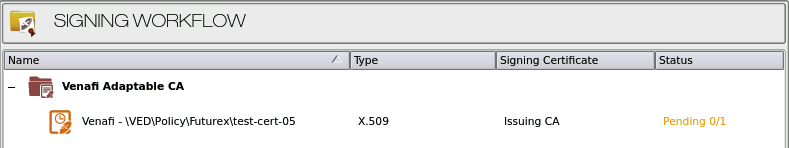
3
Right-click the pending certificate request and select Approve. You will see a pop-up that confirms the new status of the certificate request as Approved. Select [ OK ].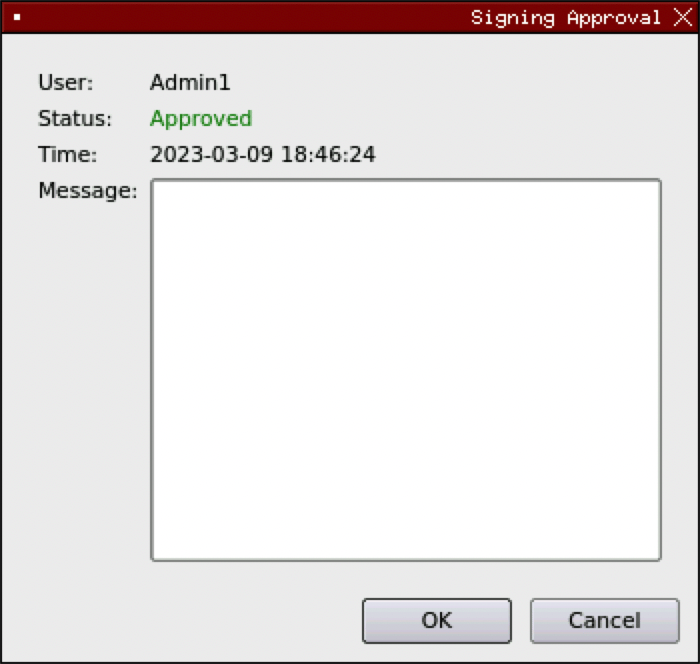
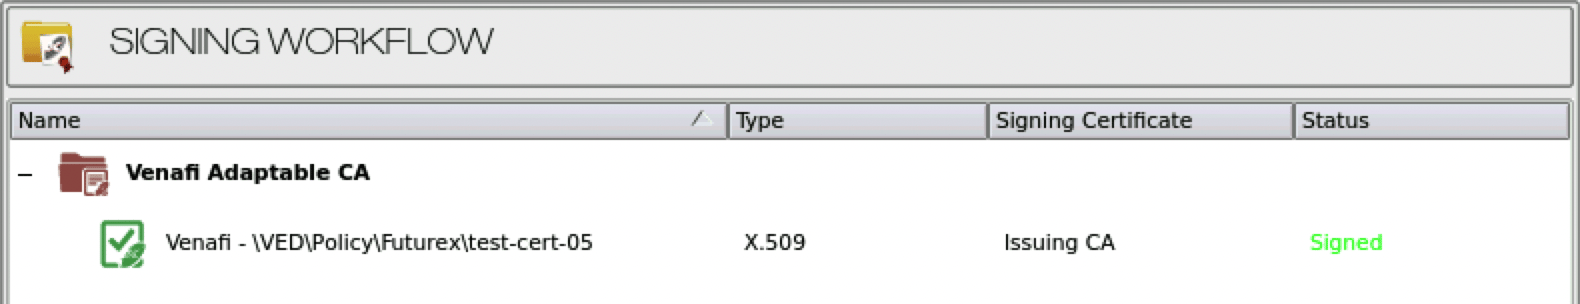
In the PKI Signing Approvals menu, the status of the certificate should show as Signed.
View the issued certificate in Venafi TPP
To view the CryptoHub-issued certificate in Venafi TPP, perform the following steps:1
Log in to the Venafi TPP web UI.
2
Select Policy Tree in the main menu.
3
Expand the policy you created in the previous section and select the relevant certificate request. The Certificate Status should show OK.